Cookie Management in an Antidetect Browser: Import and Export
Learn how Cookies work in antidetect browser profiles, how to import and export them in WadeX, and how Cookie management helps preserve isolated browser sessions.
- 1.What Are Cookies?
- 2.The Role of Cookies in an Antidetect Browser
- 3.What Happens If You Do Not Use Cookies in a New Browser Profile?
- 4.Ways to Manage Cookies in an Antidetect Browser
- 5.Importing Ready-Made Cookies
- 6.Exporting Cookies in an Antidetect Browser
- 7.Conclusion
An antidetect browser such as WadeX allows users to create separate browser profiles with isolated local data and configurable Browser Fingerprint parameters. Such environments can be useful for multi-account workflows, marketing, web application testing, and other tasks where browser sessions need to remain separated.
Cookies play an important role in these profiles. They are small pieces of data that websites store in the browser to remember sessions, authentication state, preferences, and other information.
For antidetect browser users, proper Cookie management helps maintain separate sessions across profiles and preserve their state between visits. Let’s look at how Cookies work and how they can be managed in WadeX.
What Are Cookies?
Cookies are small pieces of data that websites store in a user’s browser. When you visit a website, the server can send a Cookie to the browser. The browser stores it and, when applicable, sends it back with subsequent requests to the corresponding domain.
Websites commonly use Cookies to:
- maintain authenticated sessions;
- remember user preferences;
- save language and interface settings;
- support analytics and advertising;
- recognize returning browser sessions.
A Cookie may contain parameters such as its name, value, domain, path, expiration date, and security attributes.
For example:
name=example_cookie; value=12345; domain=example.com; path=/; Secure; HttpOnly
Depending on its configuration, a Cookie may exist only for the current session or remain stored until its expiration date or manual deletion.
The Role of Cookies in an Antidetect Browser
In an antidetect browser, Cookies are primarily part of the isolated local state of each browser profile.
When you log in to a website, Cookies can store session information so that you do not have to authenticate again every time the profile is opened. They can also preserve settings such as language, interface preferences, and other site-specific data.
Cookies can also help websites recognize a returning browser session. However, they should not be confused with Browser Fingerprinting.
Websites can analyze many signals independently of Cookies, including the IP address, HTTP headers, Canvas, WebGL, Fonts, screen characteristics, Local Storage, and other Browser Fingerprint parameters.
For this reason, Cookie management alone does not provide anonymity or prevent websites from identifying a browser environment.
What Happens If You Do Not Use Cookies in a New Browser Profile?
A newly created antidetect browser profile normally starts with little or no accumulated local data. There are no previous site sessions, stored preferences, or Cookies unless they are imported or created through normal browsing.
This is not necessarily a problem. Websites regularly receive visits from new browsers and devices.
However, Cookies may be required for normal website functionality. For example, they can preserve authentication, shopping carts, settings, multi-step forms, and other session data.
If Cookies are constantly deleted or disabled, some websites may repeatedly request authentication or lose previously saved session state.
It is therefore better to think of Cookies as one part of a browser profile’s local environment rather than as a universal way to increase account trust.
Ways to Manage Cookies in an Antidetect Browser
Creating Cookies Through Regular Browsing
The most straightforward way to create Cookies is to use the browser profile normally.
As you visit websites, accept relevant Cookie settings, sign in to services, and interact with pages, the profile gradually accumulates Cookies and other local data.
This process can also be automated with Browser Profile Warming features where available. In WadeX, profile warming can visit websites automatically and build local browser state before the profile is used for its primary workflow.
There is no universal amount of time or number of Cookies that guarantees better account quality or fewer website checks. The effect depends on the website and the signals it evaluates.
Automatic Cookie Creation
Browser automation can also generate Cookies by visiting websites automatically.
Automation tools can open pages, navigate between them, and interact with website elements. As with regular browsing, websites may store Cookies during these sessions.
Common browser automation frameworks include Selenium and Puppeteer.
However, automatically generating a large number of Cookies does not by itself make a profile more trustworthy. Websites may evaluate many additional technical and behavioral signals, and automated activity can itself be detected.
For this reason, Cookie generation should be treated as profile preparation rather than as a guaranteed method for bypassing anti-bot or anti-fraud systems.
Importing Ready-Made Cookies
Importing Cookies is a faster way to restore or transfer existing browser state into another profile.
WadeX supports commonly used Cookie formats, including JSON and Netscape.
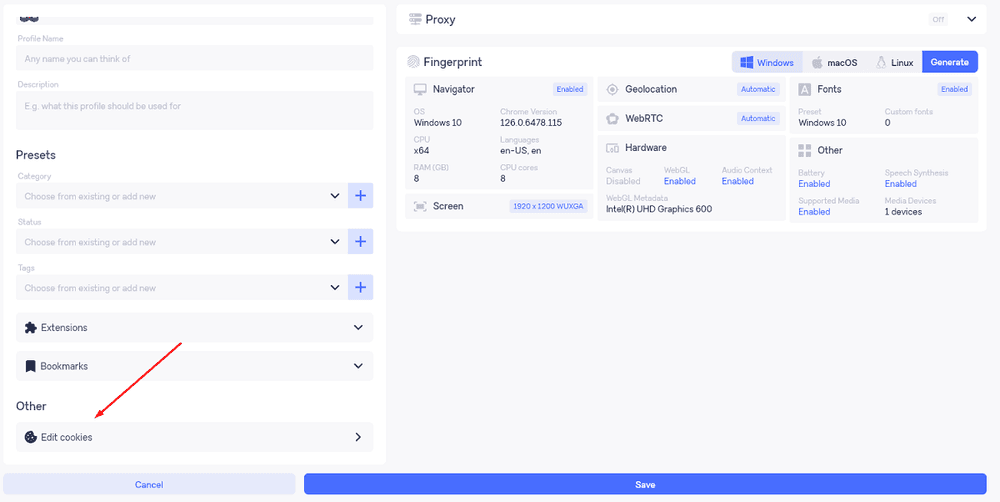
To import Cookies, open the required WadeX profile, go to the Other section, and select Edit cookie.
Click Import above the Cookie table. In the window that appears, paste the Cookie data or upload a file.
You can also specify whether existing Cookies in the profile should be removed before the new ones are imported. After configuring the options, click Import.
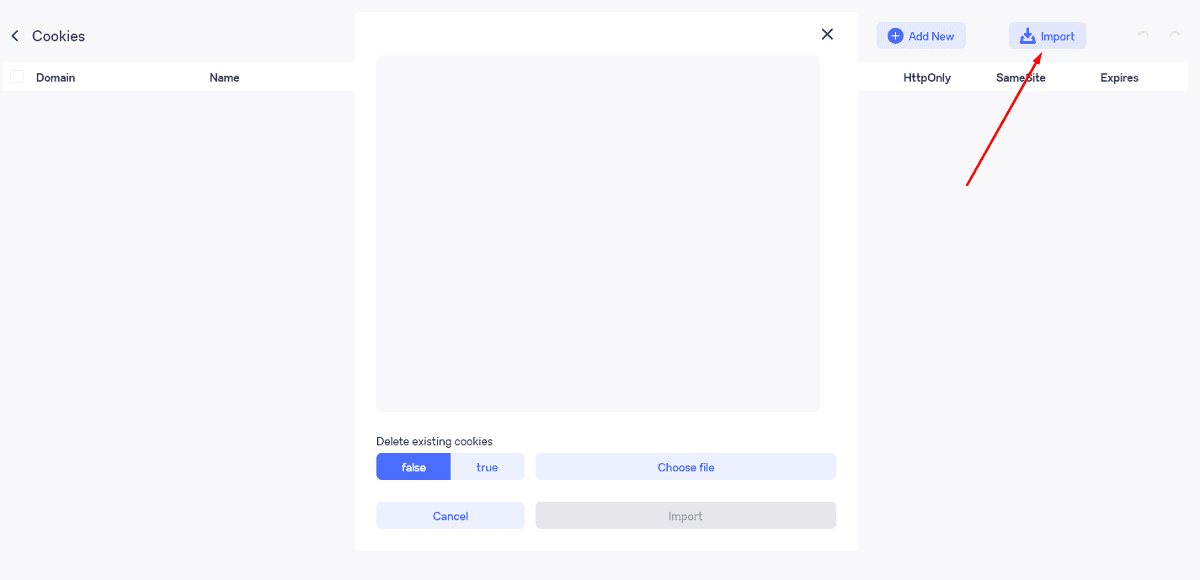
WadeX supports multiple JSON Cookie formats as well as the Netscape format, including the #HttpOnly_ prefix used for HttpOnly Cookies in Netscape-style files.
Where to Get Cookies for Import
The safest source is generally your own browser sessions.
For example, you can export Cookies from a profile or environment you control and import them when you need to restore or migrate the session.
Be careful with Cookie files obtained from unknown sources. Cookies can contain active authentication tokens and other sensitive session data. Importing or sharing them may expose accounts to unauthorized access.
For the same reason, avoid publishing authentication Cookies or transferring them through untrusted services.
Exporting Cookies in an Antidetect Browser
Exporting Cookies allows you to save browser session data and transfer it between profiles or environments when appropriate.
This can be useful for backups, testing, profile migration, and legitimate team workflows where authorized access needs to be preserved.
Why Export Cookies?
Cookie export can be useful for several purposes:
- Transferring data: Move Cookie data between profiles or devices you control.
- Creating backups: Preserve session state in case a profile needs to be restored.
- Team workflows: Transfer authorized session data when several team members work with the same resources.
- Testing and development: Reproduce a known browser state in a controlled test environment.
Because exported Cookies may include authentication information, Cookie files should be treated as sensitive data.
How to Export Cookies
Open the required WadeX profile, go to the Other section, and select Edit cookie.
Click Export cookie.
By default, Cookies can be exported in JSON format. Netscape format is also available when compatibility with other tools is required.
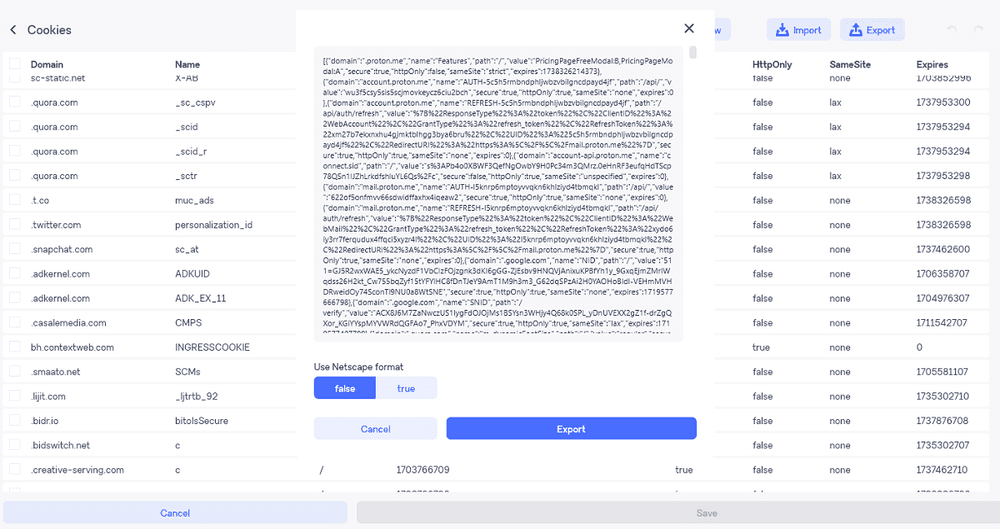
Store exported files securely, especially if they contain active login sessions.
Conclusion
Cookies are an important part of how websites maintain browser sessions. They can store authentication state, preferences, settings, and other information needed for normal website operation.
In an antidetect browser such as WadeX, Cookies are kept as part of each profile’s isolated local environment. Users can create them through normal browsing or profile warming, as well as import and export them when session migration or backup is required.
At the same time, Cookies are only one part of the browser environment. Websites may also analyze the IP address, Local Storage, Browser Fingerprint, account activity, and other technical or behavioral signals.
Effective Cookie management therefore means maintaining the required session state and keeping profiles separated — not guaranteeing anonymity or bypassing website security systems.